Google Ads measurement buying guide
Google Ads server-side tracking tools are not interchangeable. A hosting platform, a customer-controlled cloud deployment, a configured server container, a CRM upload, and a fully managed implementation solve different parts of the measurement problem. This guide helps buyers compare the real scope before choosing a product or provider.
Short answer: Choose an option by separating four decisions: who hosts the endpoint, who designs and configures the measurement, who owns the accounts and data flow, and who maintains it after launch. Compare the complete operating model—not only a monthly platform price. Require a measurement plan, consent behavior, conversion mapping, deduplication, monitoring, documentation, handover, and acceptance tests in writing.
Why “server-side tracking solution” can mean several different purchases
A buyer may ask for a server-side tracking platform and receive three very different quotations. One could cover only a hosted runtime for a server container. Another could configure a standard Google Tag Manager server container but leave event design, consent, and ongoing maintenance to the customer. A third could include discovery, implementation, Google Ads conversion mapping, CRM work, testing, documentation, and support.
Those offers should not be compared as though they provide the same result. Google’s server-side tagging overview describes moving tag instrumentation from a website or app into a server environment. The important purchasing implication is that infrastructure is only one layer. An event still needs an authorised source, an endpoint, processing rules, a destination, and a way to verify what happened.
If you need the basic concept first, read our separate explanation of what server-side tracking is and why it matters for Google Ads. This article owns a different question: what should a business buy, retain, and verify?
Do not accept a binary label. “Server-side enabled” may apply to selected events or destinations while other tags remain browser-side. Ask which events, data fields, systems, and advertising destinations are actually covered.
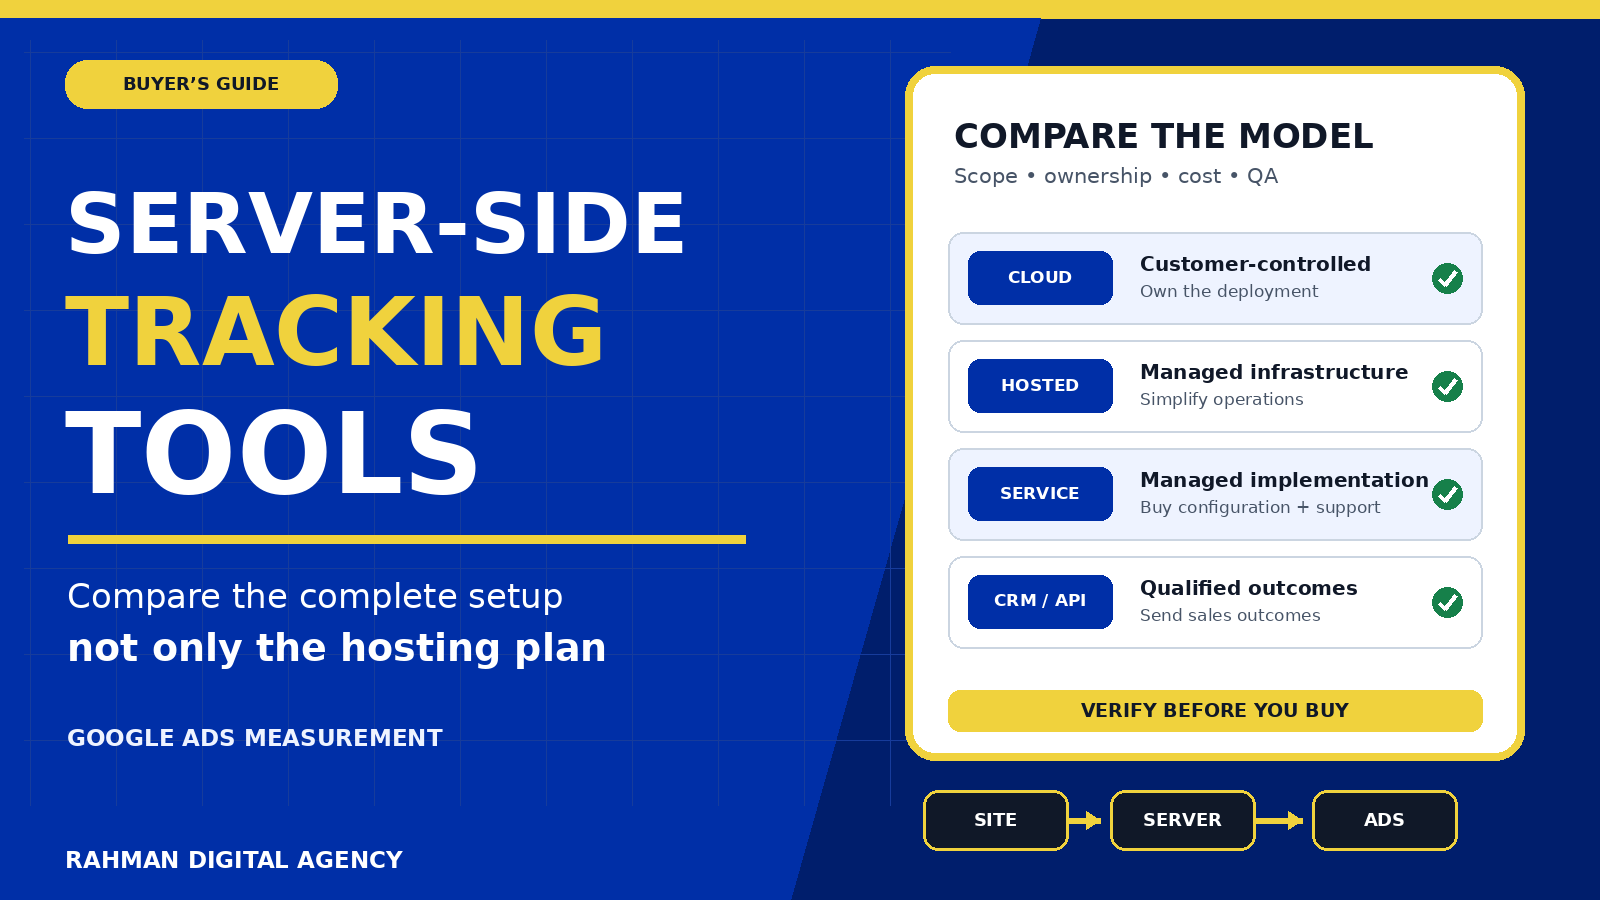
The four delivery models to compare
| Model | What you receive | What you still need | Best fit |
|---|---|---|---|
| Customer-controlled cloud deployment | A server-container runtime in a cloud project controlled by the customer | Architecture, web and server configuration, DNS, consent, testing, monitoring, updates and support | Teams that value direct infrastructure ownership and have technical capacity |
| Hosted server-side platform | Provider-operated runtime, provisioning, plan limits and usually infrastructure monitoring | Correct event design, destination tags, consent logic, QA, documentation and ongoing measurement decisions | Teams that can implement tracking but want simpler infrastructure operations |
| Managed implementation | Human discovery, configuration, testing and handover; maintenance may be included or separate | Clear client decisions, authorised access, legal review, accurate source data and an agreed operating owner | Businesses without enough internal measurement expertise or implementation time |
| Direct server-to-server or CRM integration | An application, checkout or CRM sends conversion outcomes through an API or native connector | Identity and click-ID capture, data quality, consent, retries, deduplication, reconciliation and alerting | Businesses that need qualified-lead, sale, refund or delayed-outcome feedback |
These models can be combined. A business might own the cloud project and Tag Manager accounts while an external specialist performs the implementation and maintenance. Another might use managed hosting but keep the container configuration in-house. “Managed” should describe named responsibilities, not a vague premium label.
Google’s current manual setup guidance demonstrates that a server container and deployed tagging infrastructure are separate elements. Its guide to sending data to server-side Tag Manager also shows that browser or app data must be routed to the endpoint deliberately. Buying hosting does not migrate existing tags automatically.
What should a complete implementation scope include?
Start with a measurement plan. List the business actions that matter, where they originate, which permitted identifiers are available, and where each event should go. A technical proposal that begins with containers but never defines a valuable conversion is solving the wrong problem.
Foundation and infrastructure
- Inventory of current website, app, checkout, CRM and advertising measurement
- Web or client-side Tag Manager changes needed to generate and route events
- Server container, hosting choice, deployment region, scaling and billing owner
- Custom tagging subdomain, DNS, TLS and any CDN or proxy configuration
- Access roles, service accounts, least-privilege permissions and change approval
- Development, test and production environments where complexity requires them
Google recommends mapping the tagging deployment to a subdomain of the website in its custom-domain documentation. That creates an important ownership question: who controls the DNS, certificate process and endpoint after the supplier relationship ends?
Measurement configuration
- Conversion names, triggers, values, currencies, identifiers and expected source systems
- Google Ads conversion actions and destination-specific tags
- GA4 events where they serve a defined reporting purpose
- Enhanced conversions where the business has an appropriate data and consent path
- Offline or CRM outcomes when lead quality or delayed sales matter
- Stable transaction or order IDs and a tested browser/server deduplication design
- Internal, test and staff traffic handling
A server endpoint alone is not a completed Google Ads implementation. Google publishes a separate guide for Google Ads conversions with server-side Tag Manager, because destination configuration remains necessary.
Operations and handover
- Monitoring, alert thresholds, log access and incident notification
- Container versioning, release notes, rollback and backup expectations
- Named owner for browser, server, CRM and advertising-platform changes
- Data-flow diagram, event dictionary and test record
- Administrator training and an export or migration procedure
- Maintenance scope, response time, exclusions and renewal terms
Scope test: If a proposal says “sGTM setup included,” ask whether that means infrastructure provisioning only, a working web-to-server data path, configured Google Ads conversions, consent propagation, deduplication, launch validation, documentation, and post-launch monitoring. Record every answer as included, excluded, optional, or client-owned.
Compare total operating cost, not the headline plan
There is no responsible universal price for server-side measurement. Cost changes with request volume, cloud region, availability requirements, destinations, CRM complexity, support level and how clean the current data layer is. Google Cloud’s Cloud Run pricing, for example, is usage- and configuration-dependent rather than a single “tracking” fee.
Build a three-column cost model:
- One-time implementation: discovery, measurement plan, data-layer work, container configuration, DNS, destination setup, consent integration, CRM work, QA, documentation and training
- Recurring infrastructure: hosted-platform subscription or cloud consumption, networking, logs, monitoring, storage and overages
- Recurring operations: support, incident response, tag changes, platform updates, audits, consent changes, CRM maintenance and reporting
Customer-controlled cloud does not mean unmanaged physical servers. Google describes Cloud Run as a managed compute platform. The operational work shifts: somebody still owns billing, permissions, domains, releases, logs, scaling choices and support. A hosted platform may simplify those tasks, but the proposal should state request limits, overage calculation, regions, support hours and exit terms.
Protect account ownership, access and portability
A technically sound setup can still be a poor purchase if the business cannot operate or migrate it. Decide who owns each asset before work begins:
- Google Tag Manager web and server containers
- Google Cloud project or hosted-platform account
- Tagging subdomain, DNS records and certificates
- Google Ads conversion actions and linked accounts
- GA4 property, streams and event configuration
- CRM integration, API project, service accounts and secrets
- Custom templates, code, deployment files and licences
- Logs, dashboards, test evidence and technical documentation
Prefer named user accounts and appropriate roles over shared administrator credentials. Require an offboarding path that covers account access, configuration exports, custom code, DNS changes, secret rotation, documentation and a reasonable transition window. A service can be managed without trapping the customer.
Practical default: The customer should usually control its domain, advertising, analytics and core Tag Manager accounts. Infrastructure ownership can vary, but the contract should state what can be exported, what cannot, and what happens when service ends.
Consent and data governance belong in the buying decision
Server-side processing is not a shortcut around consent, transparency or data minimisation. It gives the implementation more control over what is forwarded, which makes the field-level data map more important—not less.
Google’s consent-mode implementation guidance explains that consent mode communicates a visitor’s consent status to Google tags and interacts with a banner or consent-management platform. It does not provide the banner or make the underlying legal decision for the advertiser.
Ask the provider to document:
- Each event source, endpoint, destination and data field
- Which identifiers may be present before and after consent
- How default and updated consent states propagate to the server
- What is stored in application, access and error logs
- Retention, deletion, access control and breach-notification responsibilities
- Provider and subprocessor roles, regions and contractual documents
- How sensitive or unnecessary fields are prevented from being collected
Google says enhanced conversions supplement existing measurement with hashed first-party, user-provided data. Hashing is a security and matching measure; it should not be described as anonymisation or automatic permission to collect data. The business should obtain appropriate legal advice for its markets and actual data flow.
Define reliability, monitoring and support before launch
Measurement can fail quietly. A website can continue accepting orders or leads while a changed form, expired credential, malformed request, blocked endpoint, template update or CRM error stops useful conversion data. Ask how the solution makes failure visible.
Minimum operational questions
- What availability commitment applies to the hosted endpoint?
- How are request limits, overages, autoscaling and regional outages handled?
- Which health, error and volume signals are monitored?
- Who receives alerts, during which hours, and through which channel?
- What is the response-time commitment, and does it describe response or resolution?
- How are changes approved, versioned, tested and rolled back?
- How long are useful logs retained, and can authorised customer staff access them?
- What happens when the browser sends successfully but Google Ads or the CRM rejects the payload?
Ask for a normal operating baseline, but reject a universal promise of perfect agreement. Backend orders, Google Ads, GA4 and a CRM can differ because they use different event definitions, consent availability, attribution rules, conversion windows, time zones and processing logic. Reconciliation should explain known differences rather than force every total to match.
Choose the architecture around the business outcome
A form submission, an accepted sales opportunity and a paid invoice are different events. Sending only the first step can optimise campaigns toward volume rather than quality. The solution should match the sales cycle.
Website or checkout events
For immediate online actions, a web event routed through a server container may be appropriate. The design should carry value and currency when meaningful, use a stable transaction identifier, and prevent duplicate browser and server events. Google’s guidance on transaction IDs and duplicate conversions explains why a unique identifier matters.
Enhanced conversions
Enhanced conversions can supplement an existing conversion with permitted, normalized and hashed first-party data. They do not replace the conversion trigger, consent design or diagnostics. See our separate enhanced conversions setup guide for that feature’s specific implementation context.
CRM and offline outcomes
For leads that become qualified or close later, the relevant architecture may include CRM outcome uploads. Google documents uploading click conversions as a distinct workflow. That requires reliable click-identifier capture, sales-stage definitions, upload scheduling, error handling and appropriate consent. It is not merely another hosted server-container plan.
Our guide to offline conversion tracking in Google Ads explains that workflow in more detail. If the current foundation is incomplete, start with the GA4 and GTM conversion tracking foundation before adding architecture that increases complexity.
Require evidence-based acceptance testing
Do not accept screenshots of installed tags as proof of a working measurement system. Create a test matrix for every important conversion and retain the expected and observed result.
| Test area | Evidence to retain | Failure to detect |
|---|---|---|
| Trigger and source | Realistic test action, source event and payload fields | Event fires on page view, validation error or wrong user action |
| Routing | Expected endpoint, server client claim and destination request | Event never reaches the server or is claimed by the wrong client |
| Consent | Denied, granted and updated states for relevant regions | Unexpected identifiers or requests before consent |
| Conversion mapping | Correct conversion action, value, currency and business identifier | Wrong account, label, static value or missing order ID |
| Deduplication | Browser/server pair and repeated-page behavior | One business action counted twice |
| CRM or API | Accepted upload, rejected upload and retry path | Silent loss after rate limit, schema or credential error |
| Operations | Alert, rollback, version record and named owner | Failure persists unnoticed or cannot be reversed |
After launch, use our 15-check server-side tracking accuracy audit for detailed validation and reconciliation. No responsible provider should promise 100% tracking or a universal match-rate threshold. Browser controls, consent, identifier availability, platform rules, network conditions and business data quality all affect measurement.
Decision matrix: which model fits your team?
| Your situation | Likely starting model | Important condition |
|---|---|---|
| Strong internal tagging and cloud team | Customer-controlled cloud deployment | Assign clear operational ownership and retain monitoring time |
| Strong tagging skills but limited infrastructure capacity | Hosted platform | Confirm limits, regions, support, export and migration |
| Limited measurement expertise or a complex migration | Managed implementation | Define whether hosting and maintenance are included |
| Long sales cycle with meaningful CRM stages | Managed or internal hybrid plus CRM/offline integration | Clean sales-stage data and click-identifier capture are prerequisites |
| High ownership requirement but limited implementation time | Customer-owned accounts with external implementation and support | Contract for documentation, handover and change control |
| Simple site with low conversion volume and no clear measurement plan | Fix definitions and current tracking first | Do not add server infrastructure merely because it is fashionable |
The last row matters. Server-side architecture adds capability and responsibility. If conversion definitions are unclear, forms are unreliable, the CRM is inconsistent, or nobody owns consent and QA, adding another layer can make the failure harder to diagnose. Start with the business event and the operating owner.
Copyable questions for a platform or managed provider
- Which delivery model are you proposing: hosting, implementation, maintenance, or a combination?
- Which web, server, advertising, analytics and CRM accounts will the customer own?
- Which events and destinations are included, and which remain browser-side?
- Who creates and owns the tagging subdomain, DNS and cloud or platform account?
- How are Google Ads conversion actions, values, currencies and transaction IDs configured?
- Does the scope include enhanced conversions, offline uploads or CRM outcomes?
- How are consent states collected, passed, tested and documented?
- Which data fields are processed, logged, retained or shared with subprocessors?
- What traffic allowance, request definition, overage, region and availability terms apply?
- Who monitors failures, what triggers an alert, and what support hours apply?
- How are container, template, API and consent-platform changes tested?
- What acceptance tests will be demonstrated before handover?
- What documentation, training, exports and migration help are included?
- What recurring work is included, excluded or billed separately?
- Which claims depend on the customer’s consent rate, identifiers, CRM quality or sales process?
Ask every bidder to answer the same list. That makes scope gaps visible and prevents a low hosting price from being compared with a complete implementation and support service.
Claims to challenge before buying
- “Tracks 100% of conversions.” A server cannot create missing consent, identifiers, valid events or accurate CRM outcomes.
- “Completely bypasses ad blockers and browser privacy.” A first-party endpoint changes delivery conditions but does not remove blocking, policy, network or browser constraints.
- “Cookie-proof” or “future-proof.” Browsers, advertising APIs, consent rules and platform requirements continue to change.
- “GDPR compliant by default.” Compliance depends on the actual purposes, data fields, consent or other lawful basis, notices, contracts, retention, access and configuration.
- “Hashed data is anonymous.” Hashed user identifiers used for matching should not be presented as anonymous merely because the readable value changed.
- “No client-side tracking is needed.” Many server-side Tag Manager designs still begin with a browser or app event. Direct CRM uploads are a separate architecture.
- “The platform will improve ROAS by a fixed percentage.” Treat vendor performance numbers as context, not a promise for your traffic, consent rate, data quality or campaign strategy.
A credible provider will state assumptions and limitations, separate infrastructure from implementation, and show how the system will be verified. It will not use a complicated architecture to avoid explaining the measurement plan.
Make the purchase decision auditable
Create a one-page decision record: business outcomes, selected delivery model, account owner, data sources, destinations, consent owner, included implementation work, recurring cost components, support owner, acceptance tests and exit path. Attach the final data-flow diagram and test report after launch.
The best option is not automatically the cheapest, most technical or most managed. It is the arrangement your organisation can own, govern, verify and maintain. For some teams that means customer-controlled cloud. For others it means hosted infrastructure with internal configuration, or customer-owned accounts with a specialist managing implementation and support.
Need a scoped, testable Google Ads tracking setup?
Rahman Digital Agency can review your current measurement, separate hosting from implementation responsibilities, and define a practical path for Google Ads, GA4, Tag Manager and CRM data. Our GTM setup service focuses on clear ownership, documented configuration and verification rather than unsupported tracking promises.
Discuss your tracking requirements